This guide explains Unifor Raiding in a neutral, compliance-focused way, helping readers understand the operational, legal, and reputational considerations involved. Background sections outline what “raiding” typically means in organizational contexts and why structured verification matters. Readers also get a decision framework, requirements, and FAQs for safer handling of related investigations.
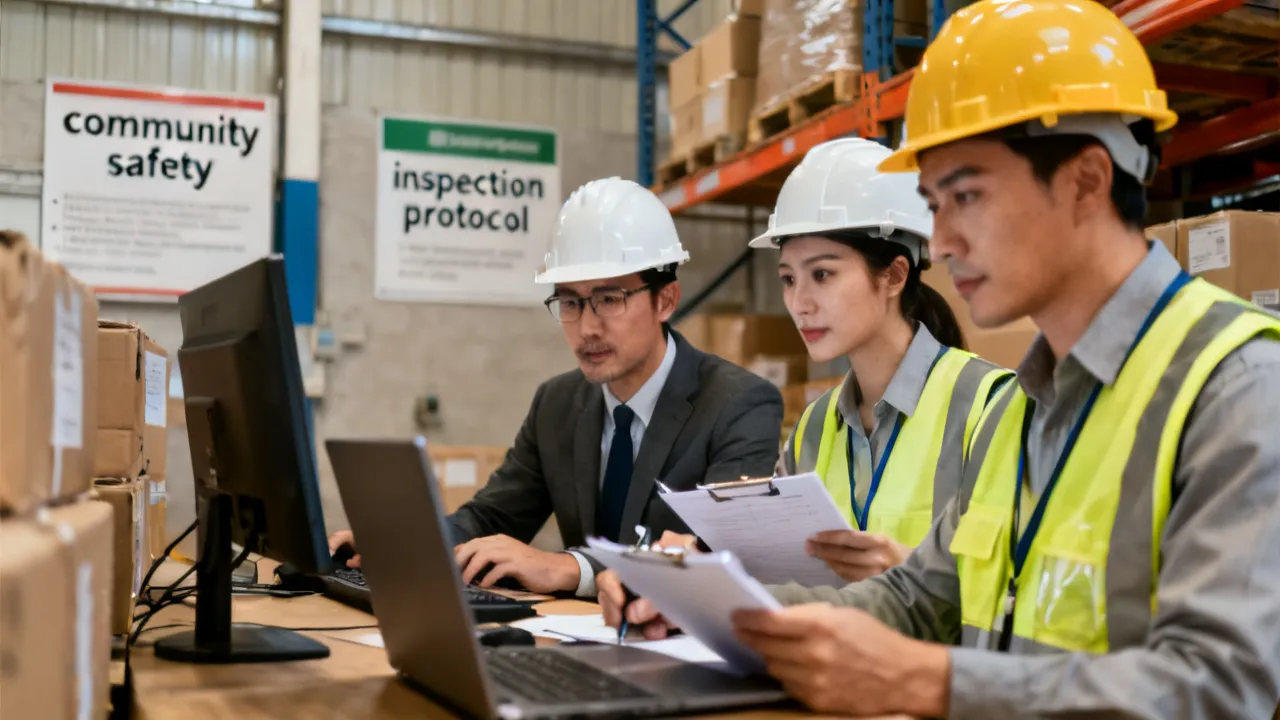
When people discuss Unifor Raiding, they are usually referring to a high-scrutiny operational action that requires careful handling, documented authority, and tight governance. From an industry perspective, the very important takeaway is straightforward: before any site visits, audits, or enforcement-adjacent activities occur, stakeholders must align on mandate, scope, evidence handling, and escalation paths. In practice, the difference between a routine compliance exercise and a damaging incident often comes down to preparation, chain-of-custody discipline, and clear communication across teams and affected parties.
Because “raiding” terminology can vary by jurisdiction and context, this article approaches the topic objectively. It does not assume wrongdoing; instead, it outlines how organizations typically manage complex inspection moments—especially when union-linked scrutiny, worker impact, and media attention are possible. If your organization is preparing for a potential interaction that resembles Unifor Raiding, treat the process like a controlled audit: define authority, standardize procedures, and verify claims with reliable documentation.
In many real-world discussions, the phrase Unifor Raiding functions as shorthand for an event that involves sudden or targeted inspection behavior with heightened stakes. Even when the intent is compliance, workers and managers often experience it as disruptive. That disruption is precisely why governance matters: investigations can change shifts, halt operations, trigger document requests, and raise concerns about process fairness.
From an operations-and-risk lens, these events commonly involve three layers:
Although Unifor Raiding may sound like a single fixed act, the practical reality is that each case depends on jurisdiction, the requestor’s role, and the reason for the scrutiny. Therefore, a compliant approach starts with clarifying the “why” and “who” before any doors open.
Organizations frequently underestimate the speed at which such events can unfold. During the first hour—when people are uncertain—risk accelerates: misstatements happen, access permissions are granted too broadly, and documents may be mishandled. To reduce this exposure, industry top practice is to create a “rapid response compliance posture” in advance.
In that posture, leadership should be prepared to answer, with evidence, at least these questions:
These steps do not “slow down” compliance—they make it safer. They also help prevent misunderstandings that could later be characterized as procedural unfairness.
Even when there is no wrongdoing, the way a response is executed can affect outcomes. A response that appears defensive or chaotic can compound friction. Meanwhile, an overly permissive approach can create confidentiality issues.
Key risk categories commonly include:
From a professional standpoint, Unifor Raiding–related interactions should be treated as a reputational event as much as a compliance event. Your communications and documentation can become part of the record.
Instead of reacting in the moment, organizations benefit from a structured decision path. The goal is to maintain neutrality while ensuring that rights, procedures, and evidence handling are respected.
This framework applies to many forms of union-linked scrutiny and related inspections. It also helps you communicate with internal stakeholders without inflaming uncertainty.
The following comparison table rephrases commonly recommended supplement information into a practical checklist. It is intended to help teams understand how outcomes differ depending on preparedness and governance—without assuming any specific case facts.
| Condition / Requirement | Better Prepared Response (Typical Outcome) | Poorly Prepared Response (Typical Outcome) |
|---|---|---|
| Mandate and scope are verified early | Less conflict, clearer boundaries, fewer disputes about access | Misunderstandings, repeated requests, and procedural challenges |
| Single liaison and standardized communications | Consistent statements; fewer contradictions in follow-ups | Conflicting narratives that may escalate reputational risk |
| Evidence handling and documentation log | Traceability improves credibility of the record | Gaps in records can hinder resolution and accountability |
| Confidential data protection steps | Reduced privacy exposure; controlled disclosures | Unintentional sharing of sensitive information |
| Worker communication and safety continuity | Lower workforce anxiety; smoother operations during scrutiny | Safety interruptions and morale damage |
| Legal/compliance escalation plan | Faster resolution of authority and interpretation questions | Delays; increased likelihood of procedural errors |
This article is grounded in widely used compliance and investigation principles: verification of authority, evidence integrity, privacy/confidentiality safeguards, and documented decision trails. For regulatory context, readers should consult their jurisdiction’s labor, privacy, and workplace safety frameworks, as well as relevant guidance from recognized authorities and professional bodies.
Where statistical claims are needed, rely on official labor departments, privacy regulators, or established industry research organizations. This article avoids unverified numerical assertions because Unifor Raiding–type events are highly situational, and published numbers may vary by definition and timeframe.
Below is a practical sequence you can integrate into your compliance playbook. The emphasis is on control, clarity, and traceability—so that your response is neutral and defensible.
Preparation is where most organizations win or lose before any door opens. A “good” response is often just a well-practiced process applied under pressure. The most common failure mode in high-scrutiny events is improvisation: staff members respond based on personal interpretations or incomplete understanding of what is being asked for and why.
Preparation also means aligning the “story” internally around facts. You do not need a rehearsed script for accusations; you need a rehearsed process for requests. In many incidents, the organization later regrets the lack of a neutral timeline—because timelines are what settle disputes about what occurred first.
When scrutiny appears imminent, your priority is to reduce chaos. Even if you suspect the inquiry is unauthorized, you should still conduct the first moments with professionalism because initial impressions influence how events later get interpreted.
Stabilizing also involves the internal environment. Supervisors should prevent rumor cascades (e.g., “They’re here for wrongdoing,” “We’re being shut down,” “Everyone gets interrogated”). A short, factual internal message like “We’re confirming the scope and authority, and we’ll provide updates through designated channels” can reduce panic and behavior that later becomes problematic.
Access management is a core compliance checkpoint. The objective is not to obstruct legitimate scrutiny; the objective is to ensure the access is consistent with the stated scope and that confidentiality and evidence integrity are maintained.
Controlled access can feel restrictive to those who want immediate answers, but it usually reduces conflict. Inspectors often understand controlled processes because they mirror how legitimate audit systems work. The goal is to make the process predictable and fair.
Documentation is the difference between “we thought we complied” and “we can prove compliance.” During an event, you often cannot rely on memory, because stress reduces accuracy. A contemporaneous log builds credibility and reduces later disputes.
A useful practice is to create two layers of documentation: (1) a detailed event log, and (2) a clean “final meeting summary” that can be shared internally with relevant stakeholders. The final summary should be factual, consistent, and limited to what occurred, not what someone suspects occurred.
Many organizations treat the event as concluded once the visitors leave. In reality, the compliance burden continues: you need to analyze whether the response protected rights, maintained evidence integrity, and met confidentiality requirements.
Debriefing should also include an honest look at communication breakdowns. For example: Did multiple people provide conflicting answers? Did someone allow access beyond scope? Did staff inadvertently discuss sensitive topics? These issues can often be corrected through training and clearer operational controls.
Because Unifor Raiding is used as shorthand for events that may involve inspection or inquiry, teams should plan for common requirements. These are presented as general conditions—not as assumptions about any single case.
Not every event will include all these conditions, but the more of them you can handle proactively, the more stable and defensible your response becomes.
While the step-by-step guide provides a practical response path, organizations often need additional depth in specific compliance checkpoints. The following sections expand on areas that commonly generate disputes or create avoidable risk. These checkpoints are designed to help teams think like investigators and like privacy professionals at the same time—without drifting into adversarial behavior.
Authority verification is not merely about “asking for documents.” It is about ensuring that the request aligns with the organization’s obligations and the requester’s jurisdictional role. In many incidents, the turning point is not the content of the request but whether it was made under a recognizable mandate.
To implement authority verification as a minimum viable check, organizations can:
Authority verification should be done immediately. Delays often cause staff to fill in gaps with assumptions, and assumptions later become credibility problems. Even if you ultimately decide to grant access, you want to do so under clearly understood authority.
Scope control is not only about avoiding conflict; it directly reduces privacy and confidentiality risk. Employees frequently have different levels of expectation regarding what is private and what is work-related. If a request is within scope, it may still require privacy safeguards.
Common scope control failures include:
A robust scope control approach includes a scope “mapping” step: identify what records correspond to the requested categories and ensure only those records are retrieved. That map should be prepared in advance (during peacetime), so in a crisis your team can respond quickly.
Evidence integrity is central in inspection-adjacent events. Even when no formal legal dispute is anticipated, organizations should assume that recorded materials could later be reviewed by external parties.
Evidence integrity depends on:
Chain-of-custody discipline also matters for physical documents. If pages are copied, stapled, scanned, or handed over, the process should be logged. If you later cannot prove how a set of documents was assembled, opponents may challenge the integrity of the evidence.
Privacy is both a legal and ethical checkpoint. It is also a workforce relationship checkpoint. If employees feel that their personal information was casually exposed, trust erodes and the incident may become a broader organizational crisis.
Organizations can strengthen privacy handling by doing the following:
In many disputes, the most defensible position is that you provided what was requested within scope while protecting confidential information through a disciplined method. A clear process reduces the chance of accusations that confidentiality was ignored.
Unifor Raiding–type events may be perceived as coercive even if the intent is compliance. That perception can increase anxiety, affect morale, and disrupt safety routines.
To protect worker impact and safety continuity, prioritize:
Worker impact also includes operational scheduling. If the event disrupts shifts, communicate internally to avoid rumors and ensure predictable schedules. Predictability reduces fear and reduces “on-the-spot” behavior that can complicate investigations later.
When scrutiny begins, communications become a compliance tool. If communications are chaotic, later testimony can conflict. If communications are defensive, it can fuel narrative harm. If communications are neutral and consistent, it reduces reputational damage.
Practical communications governance can include:
Communications should never undermine privacy. Even internal communications should be need-to-know. A common mistake is distributing the entire event narrative broadly, which can spread sensitive details.
Escalation is not a sign of weakness. It is a sign of maturity. But escalation needs thresholds and triggers to avoid unnecessary delays.
Possible escalation triggers include:
Once counsel is involved, ensure counsel has access to the event log and scope mapping. Counsel can’t advise effectively if the organization’s factual record is incomplete. Similarly, counsel involvement should not stop documentation; documentation remains essential.
In modern environments, many compliance requests eventually touch digital systems—email archives, shared drives, HR platforms, scheduling tools, and incident reporting systems. Digital access requests are where unstructured action can cause major privacy and evidence integrity issues.
Teams should plan for digital access by implementing:
Another digital checkpoint is email and messaging platforms. Even if you believe content is relevant, email and chat logs can include third-party personal data. Your retrieval process should account for that and ensure privacy safeguards are applied.
Many investigations fail not because actions were improper, but because timelines were unclear. People remember events differently. Documentation standardizes memory.
A recommended practice is to produce:
These outputs should be consistent with each other. If the final meeting summary contradicts the detailed log, credibility declines and disputes intensify.
Post-event actions are often overlooked. But the organization’s defensibility depends on what happens next.
Key post-event steps include:
Retention must align with local regulatory and internal policies. If your organization deletes records after a routine schedule, but a legal hold applies, deletion should be paused for relevant categories under counsel guidance.
Because real-world events vary, teams often ask the same set of practical questions. The answers below expand on the earlier FAQ sections, using process-focused language rather than jurisdiction-specific legal advice.
Do not proceed based on assumptions. Ask for the scope in writing or a clear list of locations, systems, and documents requested. When scope changes, update the event log and adjust access boundaries accordingly. If the requestor cannot clarify, escalate to compliance counsel. Your goal is to keep the process aligned to an explicit scope definition.
Inform employees calmly about the event process and encourage them to direct questions through the designated liaison. If interviews are conducted, ensure safe and respectful conditions and document who asked what and when—within the boundaries of privacy and internal policy. Avoid asking employees to “confess” or to coordinate stories. Instead, focus on accurate statements and compliance with non-retaliation principles.
Often, redaction is a lawful and privacy-preserving response to provide responsive content while protecting sensitive personal data. However, whether and how redaction is acceptable depends on scope, authority, and applicable privacy rules. The defensible approach is to apply redactions consistently using documented criteria and to record why each redaction category was applied.
Treat them as high-sensitivity categories. Escalate to legal/compliance counsel. Confirm mandate and scope, then provide only what is necessary and permitted. If access is not clearly authorized, document the reasoning for withholding and offer an alternative method (e.g., summary reports rather than detailed personal records) if permitted.
Do not ignore the request reflexively. Instead, verify authority and scope and request clarification. If unauthorized access is apparent, counsel guidance can determine how to respond (e.g., whether to deny entry to certain areas or maintain controlled observation). Document the challenge process and keep the interaction neutral.
Apply a clear policy: either prohibit recording in certain areas or require supervised recording only where permitted. Ensure that filming rules align with safety, privacy, and confidentiality expectations. Document whether recording was allowed and under what conditions.
Safety compliance should never be bypassed. Require escort, PPE, and adherence to site safety procedures. If inspectors insist on unsafe movement, document the request and refusal and escalate immediately to safety leadership and counsel if needed.
Avoid speculative explanations and avoid concluding wrongdoing. Instead, focus on describing your documented processes: “We have procedures for X,” “We track documentation through Y,” “We can provide records from the custodian,” and “We will confirm scope before sharing.” If questions require factual detail, route them through the liaison and ensure statements are consistent with the evidence log.
Costs vary widely based on scope, legal complexity, document volume, and whether external counsel or independent advisors are engaged. If you are budgeting, treat it as a scenario-based exercise rather than relying on a universal “price.” For accurate planning, consult internal finance and, when needed, obtain quotes from qualified compliance or legal providers.
Jurisdiction and local workplace practices influence procedural expectations—especially around privacy, labor compliance, and workplace safety. When communicating publicly, use careful language and avoid region-specific assumptions. (If you encounter location-based terminology in your source materials, verify what the term means locally before acting.)
If your organization is preparing for a Unifor Raiding–type scenario, the very reliable strategy is disciplined preparedness. By treating the interaction as a controlled compliance process—rather than an emotional reaction—you reduce legal uncertainty, minimize workforce disruption, and support a defensible, professional outcome.
Understanding Unifor Raiding through a governance lens helps organizations respond with neutrality, clarity, and documented control. While the term may be used informally, the operational principles are consistent: verify authority, define scope, protect confidentiality, maintain evidence integrity, and communicate through a single controlled channel. With a step-by-step preparedness plan and clear requirements, teams can handle scrutiny with fewer surprises and more trust from internal stakeholders.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You

Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
The Guide to Car Trading

Smart Strategies to Slash Costs on Your Roof Replacement Endeavor
Opening Remarks: Smart budgeting doesn't mean cutting corners on quality. This guide will delve into cost-effective approaches for roof replacement that maintain high standards.

Unlocking the Secrets of Preschool: Your Ultimate Guide to Early Childhood Education Programs
The significance of early childhood education programs is paramount in shaping the foundational stages of a young child's life. These educational experiences aim to furnish children with a diverse skill set before they face the structured environment of elementary education. Such programs offer a dynamic and engaging atmosphere where children's natural curiosity leads to the broadening of their thought processes. Moreover, they focus on rectifying behavioral patterns and fostering positive principles and routines.
Enhance Your Smile: Essential Gum Care Tips After Teeth Replacement
After getting new dental implants, it's crucial to look after your gums to aid recovery, shield against infection, and enhance the durability and function of the implants. This discussion delves into the key methods and top tips for gum care that are vital to keep your gums robust and healthy after your procedure.
Unlock the Secrets to Championing Fair Pay: A Guide to Fighting for Competitive Nurse Salaries at Your Hospital
To effectively navigate the intricacies of nurse compensation in healthcare institutions, a thorough understanding goes beyond the basics. Strategic advocacy is essential, honoring nursing as a critical profession while also deeply comprehending the economic aspects of healthcare. This article lays out systematic methods to advocate for fair remuneration for nurses, aimed at closing the divide between managerial policies and the realities nurses face daily.
Protect Your Golden Nest Egg: Smart Strategies and Essential Precautions for Securing Your Gold Investments
Investing in gold requires more than just purchase; diligent protection and a strategic mindset are crucial. A secure gold investment is built on thoughtful planning, alert risk management, and the capacity to adapt to changes. We'll explore various ways to protect these investments from the diverse challenges they face.
Unlock Higher Earnings: Master the Art of Leveraging Your Nursing Expertise for a Hefty Pay Raise!
Unraveling the complexity of the payment landscape in nursing isn't for the faint-hearted, yet it's a manageable task with a strategy in place, enhancing one’s prospects for improved salary through skill and knowledge. This delicate dance of upholding patient care while seeking just rewards is a path all nurses must walk. Grasping the elaborate character of the nursing role and what propels one's income forward is crucial. Within this paper, we dissect insightful methods to maximize the impact of your nursing qualifications.